DDoS Protection for Businesses
DDoS attacks bring websites and online services to a standstill — with increasing frequency and complexity. With cloud-based mitigation, WAF and 24/7 monitoring we work to keep your systems available.
Why DDoS Protection?
Availability is business-critical
Cloud Mitigation
Cloud-based DDoS mitigation absorbs attack traffic of up to several terabits per second in the mitigation network, before it reaches your infrastructure.
Protecting Availability
Attack traffic is absorbed in the mitigation network before it reaches your infrastructure. The goal: your website and online services stay usable even during an attack.
Instant Detection
Automatic detection of DDoS attacks within seconds — with immediate activation of countermeasures.
Web Application Firewall
The WAF protects against application-layer attacks (Layer 7) such as HTTP floods, Slowloris and bot attacks.
Traffic Analysis
Intelligent traffic analysis distinguishes legitimate users from attackers and keeps false positives low.
24/7 Monitoring
Cloud mitigation and traffic analysis run automatically around the clock and step in immediately when patterns look suspicious. Assessment and fine-tuning are handled by your dedicated contact.
DDoS Mitigation
Traffic Analysis
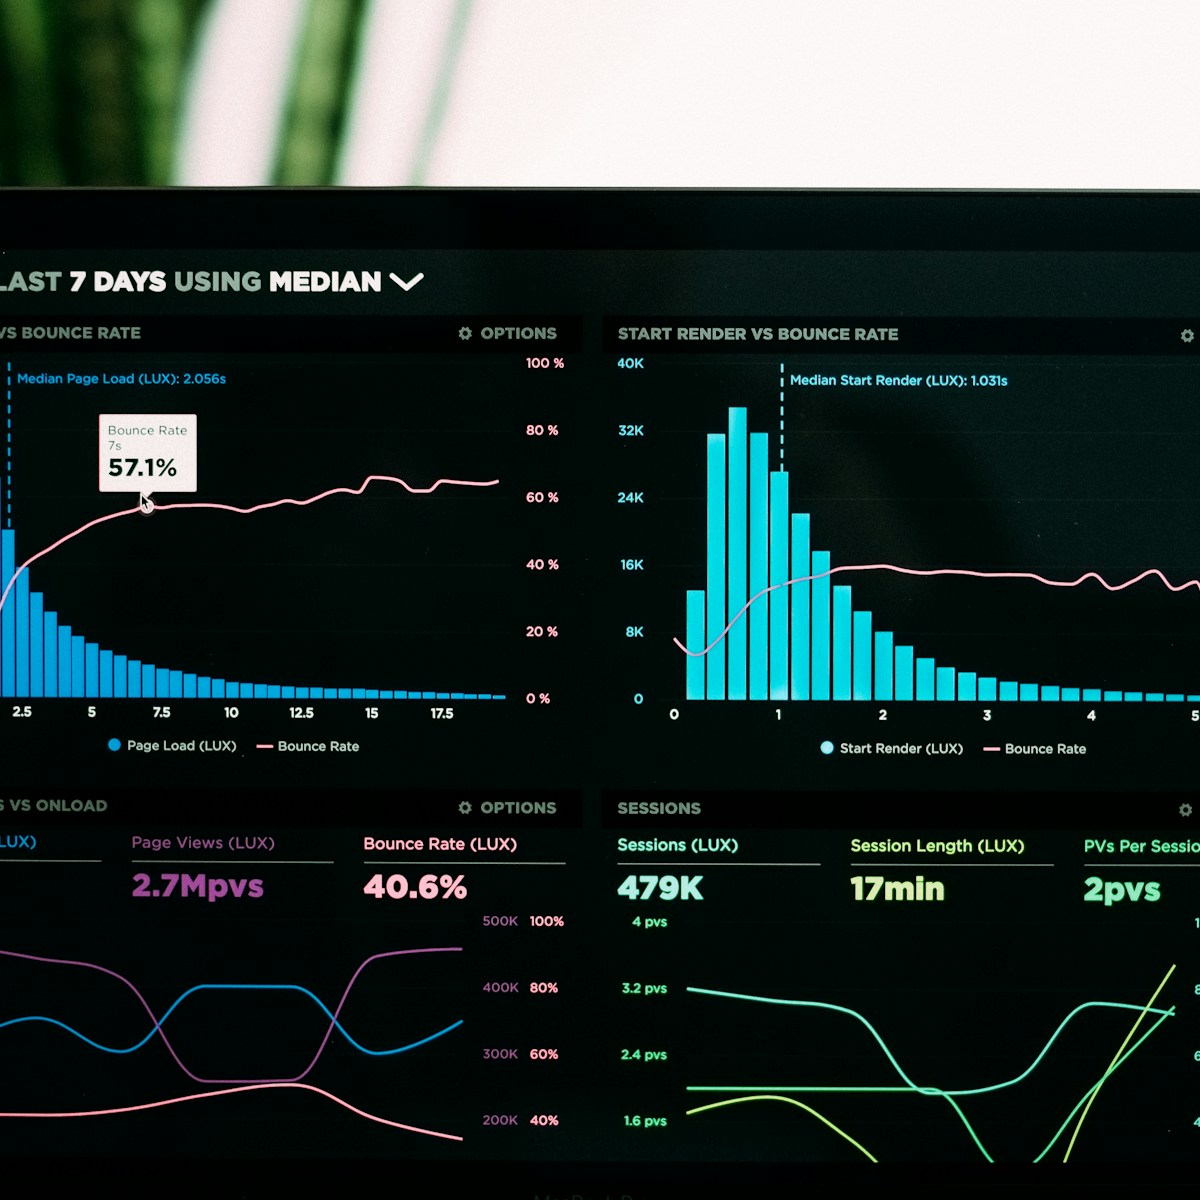
Real-Time Monitoring
Filtering attack traffic in the mitigation network
Automatic traffic filtering with 15 Tbps capacity. Layer 3/4/7 protection with rate limiting, geo-blocking and intelligent traffic analysis.
Our DDoS Protection Services
Multi-layered protection for high availability
DDoS Mitigation
Cloud-based absorption of volumetric attacks with global Anycast infrastructure and high filtering capacity.
Web Application Firewall
Layer 7 protection against HTTP floods, SQL injection, cross-site scripting and other application-layer attacks.
Anomaly Detection
AI-powered baseline analysis of your normal traffic to detect deviations and attack patterns.
Load Distribution
Load balancing and geo-redundancy improve the availability of your services even during partial outages.
Bot Management
Detection and blocking of malicious bots while allowing SEO crawlers and legitimate bots through.
Network Hardening
Rate limiting, SYN flood protection and BGP blackholing for comprehensive network protection at Layer 3/4.
Business Continuity Plan
A documented plan for emergencies: escalation paths, failover procedures and communication strategies.
DDoS Stress Tests
Controlled DDoS simulations test your defensive capability and identify weaknesses in the infrastructure.
Related Services
Matching services that complement your project
Frequently asked questions
The questions we are asked most often before a project – with answers on process, costs and data protection.
What is a DDoS attack?
A DDoS attack (Distributed Denial of Service) floods your servers with millions of simultaneous requests, making your website and online services unreachable. DDoS attacks can last from hours to days and cause significant revenue losses and reputational damage.
How common are DDoS attacks on German companies?
DDoS attacks are increasing sharply. The BSI (Germany's Federal Office for Information Security) records thousands of attacks on German companies and public authorities every year. E-commerce, financial service providers and critical infrastructure are particularly affected. The attacks are becoming increasingly complex and leverage IoT botnets.
What DDoS protection does NovaCon offer?
NovaCon implements multi-layered DDoS protection: traffic analysis and anomaly detection, cloud-based DDoS mitigation, Web Application Firewall (WAF), load distribution and redundancy, business continuity planning and automated 24/7 monitoring as part of our SOC-as-a-Service; alerts are assessed by your dedicated contact.
Ready for the next step?
Let's discuss in a free initial consultation how we can move your business forward.